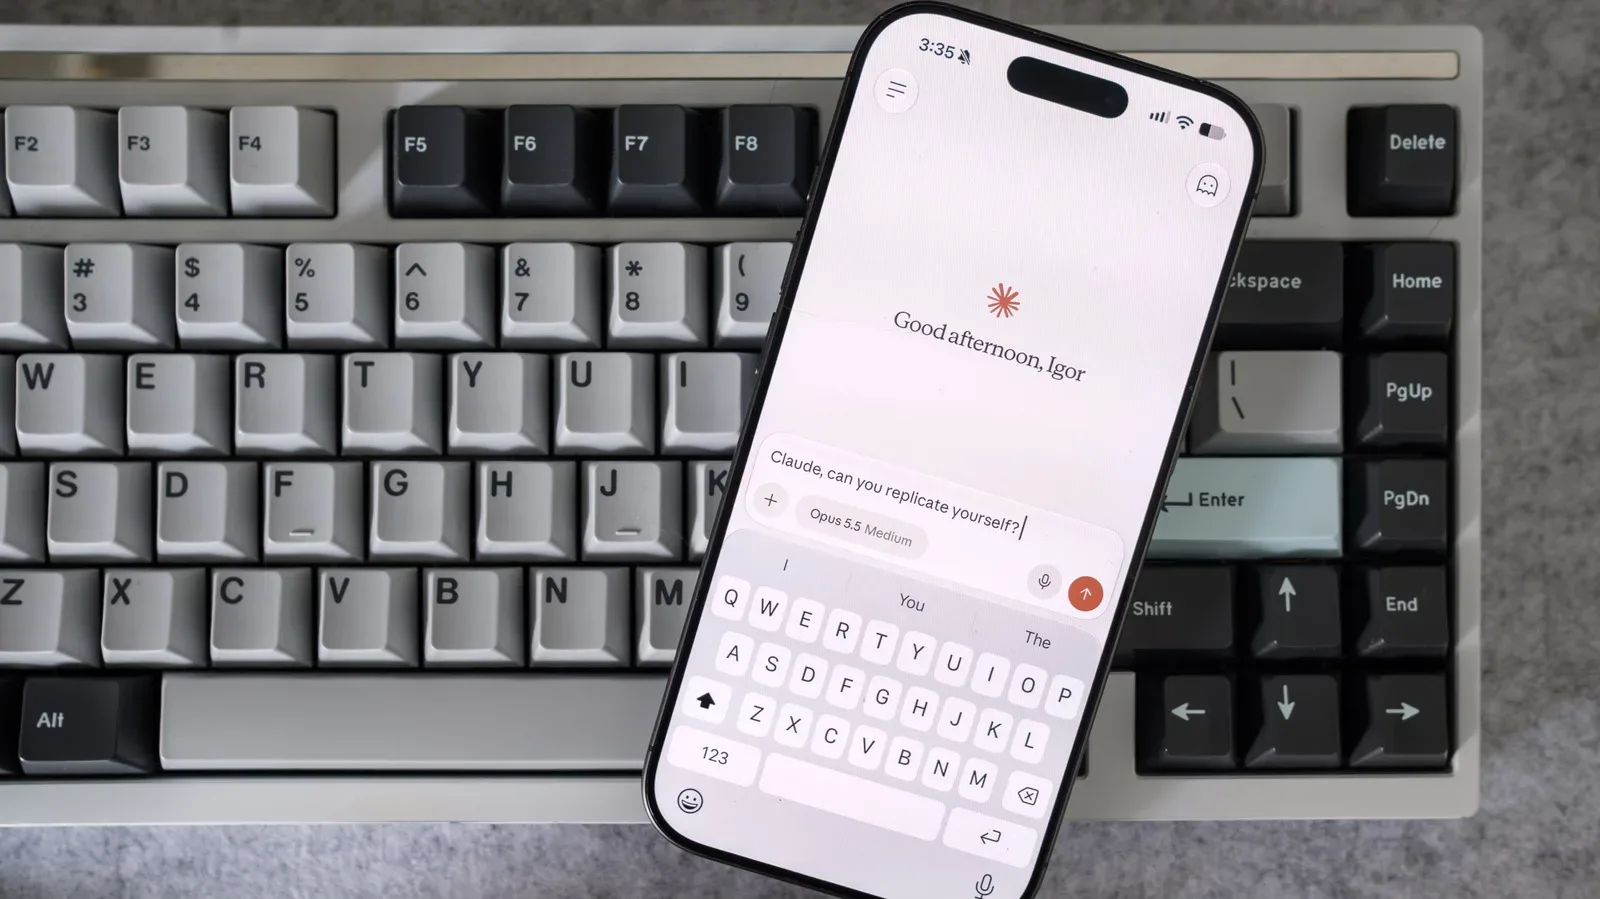
The frightening phrase is “self-replicating AI,” but the more useful way to understand the latest warning about AI-enabled botnets is considerably less cinematic. Small AI models may soon help malicious operators move through insecure connected devices with less human labor. That is a serious prospect. It is not, however, evidence that the internet has suddenly acquired an entirely unprecedented class of threat with an entirely unprecedented remedy.
The essential issue remains the vast number of poorly secured devices already connected to home and business networks: routers, internet-connected cameras and other Internet of Things, or IoT, hardware. AI could alter how quickly attackers adapt malicious software to those devices. It does not erase the importance of the old weaknesses that give attackers their first foothold.
That distinction matters for anyone whose gaming setup shares a network with a router, smart television, camera, streaming device, PC, console or phone. “AI worm” is a catchy label, but security decisions should be based on what has actually been demonstrated, what remains uncertain and which practical protections work regardless of how sophisticated the attacker’s tools become.
What the research is warning about
Anthropic’s Frontier Red Team has published research suggesting that relatively small AI models could be months away from spreading across insecure devices and creating autonomous botnets that are slow-moving but difficult to remove. A botnet is a collection of compromised computers or connected devices controlled as a group by an attacker. Those devices can be used for a range of malicious activity, including a distributed denial-of-service attack, or DDoS, in which a huge volume of coordinated traffic overwhelms a target service.
The forecast is not being dismissed outright by cybersecurity specialists. Chris Canal, chief executive of EquiStamp, said that self-replicating models are a real future possibility and suggested the relevant timeline may be arriving earlier than he would have expected. He also pointed to the rapid pace of model improvement, including AI labs using their own AI tools in machine-learning research.
Michael Bailey, a professor at Georgia Tech’s School of Cybersecurity and Privacy, likewise considers capable self-replicating models a future reality. But he argues that the exact form they take, as well as their consequences, remain open questions. That is a critical qualification. “Could happen” is not the same claim as “has been demonstrated at broad real-world scale,” and the gap between those two propositions should not get lost in the conversation.
The demonstrated scenario involved a model moving among devices and setting up inference, the process of running a trained AI model to generate outputs. Yet it was conducted in an emulated network, and the exploit used to enter devices was described as trivial. An emulated network is a controlled simulation rather than the disorderly, inconsistent and defended environment of the public internet. It can be useful for research, but it does not automatically establish how reliably an attack would perform against real systems.
Why Mirai remains the important reference point
The most useful historical comparison is not a hypothetical AI apocalypse. It is Mirai, the botnet malware that showed how everyday IoT gear could be assembled into a meaningful attack network. Bailey, who co-wrote Understanding the Mirai Botnet in 2017, has studied internet worms since the early 2000s and botnets more recently.
Related coverage includes AI Botnets May Be Closer, but Old Security Failures Remain the Bigger Risk.
Mirai was used by cybercriminals to gather IoT devices into a botnet and launch a DDoS attack against Sony’s PlayStation Network. The incident also affected Dyn, then one of the largest DNS providers in the United States. DNS, or the Domain Name System, is the infrastructure that helps direct domain names to the internet addresses computers use. When a major DNS provider is disrupted, the impact can spread far beyond the originally intended victim.
In 2016, disruption linked to that attack knocked services including Amazon, GitHub, PayPal, Reddit and Twitter offline for many users in the United States and parts of Europe. Sony estimated a loss of roughly $2.7 million in net revenue. For players, the episode is a reminder that a gaming network can be affected even when a console, account or game server is not the initial target. Major online systems depend on a long chain of outside infrastructure.
Mirai’s lesson was that apparently modest household hardware could be valuable to attackers. Cable routers and IP-enabled cameras were not merely awkward appliances with outdated settings; in large enough numbers, they could become a distributed source of traffic and computing power. That remains a durable security lesson because connected-device ecosystems have not stopped growing.
There is also a more mundane maintenance lesson. Digital life already demands a little housekeeping, whether that means checking device firmware or dealing with files left behind by software. As with the problem explored in uninstalled games still taking up storage space, the inconvenience is easy to ignore until it turns into a larger problem. Network hygiene is less visible than clearing a drive, but much more consequential when neglected.
Adaptable is not necessarily self-replicating
The most important technical dispute is over the word “self-replicating.” Traditional internet worms can copy their code from one system to another and execute the new copy. Some are polymorphic, meaning they can alter their signatures and behavior, making them harder to identify with simple pattern matching.
Bailey argues that the research’s framing is not a clean match for that model of propagation. Rather than placing a full copy of itself onto each newly compromised device, an AI-enabled botnet may be closer to a dropper. A dropper is malware that establishes access on a device and installs other code. In this possible arrangement, a compromised machine might receive a small coordination component while instructions or model capability remain elsewhere in the wider network.
That is not a trivial semantic complaint. It changes what defenders should expect. A fully self-contained copy running independently on every infected device presents one kind of cleanup problem. A distributed arrangement, in which devices carry smaller components and receive direction from elsewhere, presents another. Both can be dangerous, but precision helps avoid planning for the wrong threat.
Bailey also notes that Mirai already worked across heterogeneous hardware. In plain language, it could target different kinds of devices, including routers and cameras using different chip architectures. Its adaptability had limits: supporting a new architecture still required a human to do work such as recompiling malware. The potential step forward from AI is not that variation among devices suddenly exists. The potential step forward is automation: models may reduce the human effort required to adjust an attack to unfamiliar technical environments.
That is why Bailey describes the change as a redistribution of work between attackers and defenders rather than a wholly new malicious capability. Lowering the labor and expertise needed to build or adjust botnet tooling can change the economics of abuse. More attackers may be able to attempt it, or established attackers may operate more efficiently. But the actual damage still depends on vulnerabilities, exposed devices and defensive failures.
What was not shown
The research did not show a model retraining itself into a genuinely polymorphic threat. Copies of the model could pass notes to successors and improve the process of setting up inference over time. That is noteworthy. It is not equivalent to a model modifying and retraining itself to change its own signature and behavior in the way a polymorphic worm might.
This is not a reason for complacency. It is a reason to separate a warning about a developing capability from a claim that the final, most alarming version already exists. The near-term concern is that increasingly capable models could assist with operational work that previously took more skilled human effort. The unsupported leap would be to assume that every label associated with a classic worm already applies in full.
Canal has also raised a difficult limitation for model-focused defenses. In work with the AI-safety nonprofit FAR.AI, EquiStamp found that commonly discussed methods of removing safeguards from an open-weight model could be bypassed. An open-weight model is a model whose learned parameters, or weights, are available for others to use and modify. If a malicious actor can alter or strip protections from a model, safety measures built into that model alone are a fragile last line of defense.
That makes system security more important, not less. The relevant question cannot just be whether a model has been instructed not to behave maliciously. Defenders also need to ask whether devices are patched, whether insecure services are exposed, whether passwords are easily guessed and whether a compromised device can freely reach the rest of a network.
The boring response is still the right response
The proposed mitigations are conspicuously familiar. Internet service providers could notify customers when infection is detected and restrict infected customers to a limited set of safe websites until the problem is addressed. A version of that strategy was used during Mirai. Regulation can also reduce obvious exposure: the UK’s PSTI Act bans easily guessable default passwords on IoT devices.
For households and small organizations, the defensive priorities described by Bailey are traditional systems-security practices:
- Apply patches to routers, cameras and other connected gear when updates are available.
- Use strong, unique passwords, especially replacing factory-default credentials on devices that permit it.
- Isolate devices where possible, limiting what an IoT device can reach if it is compromised.
- Practice basic security hygiene rather than assuming AI-specific controls will solve insecure infrastructure.
“Hardening” a device means reducing the ways it can be compromised: keeping its software current, removing weak settings and restricting unnecessary access. It is not glamorous, and it does not produce a convenient single purchase that fixes every risk. But hardened devices raise the cost and difficulty for misbehaving agents and conventional malware alike.
For game players, that means treating the home network as part of the setup, even if it is rarely discussed alongside controller settings, storage upgrades or display calibration. A console may be well maintained, but it shares an environment with other devices. The practical aim is not to become a cybersecurity analyst; it is to avoid leaving the easiest door unlocked.
AI may accelerate an old problem
There is room for both concern and restraint here. Small models capable of helping attackers adjust operations across insecure devices could increase the frequency or resilience of botnet activity. Experts broadly see the general direction as plausible. At the same time, the claims being debated do not establish an entirely new category of internet danger, and the research has limits that matter when assessing the “self-replicating” label.
The larger warning is less about machines becoming magical and more about security debt becoming expensive. Networked devices with weak passwords, delayed updates and poor isolation were already useful to attackers. If AI lowers the amount of human work needed to exploit that reality, the best response remains to close the familiar gaps before attackers get a faster way to find them.