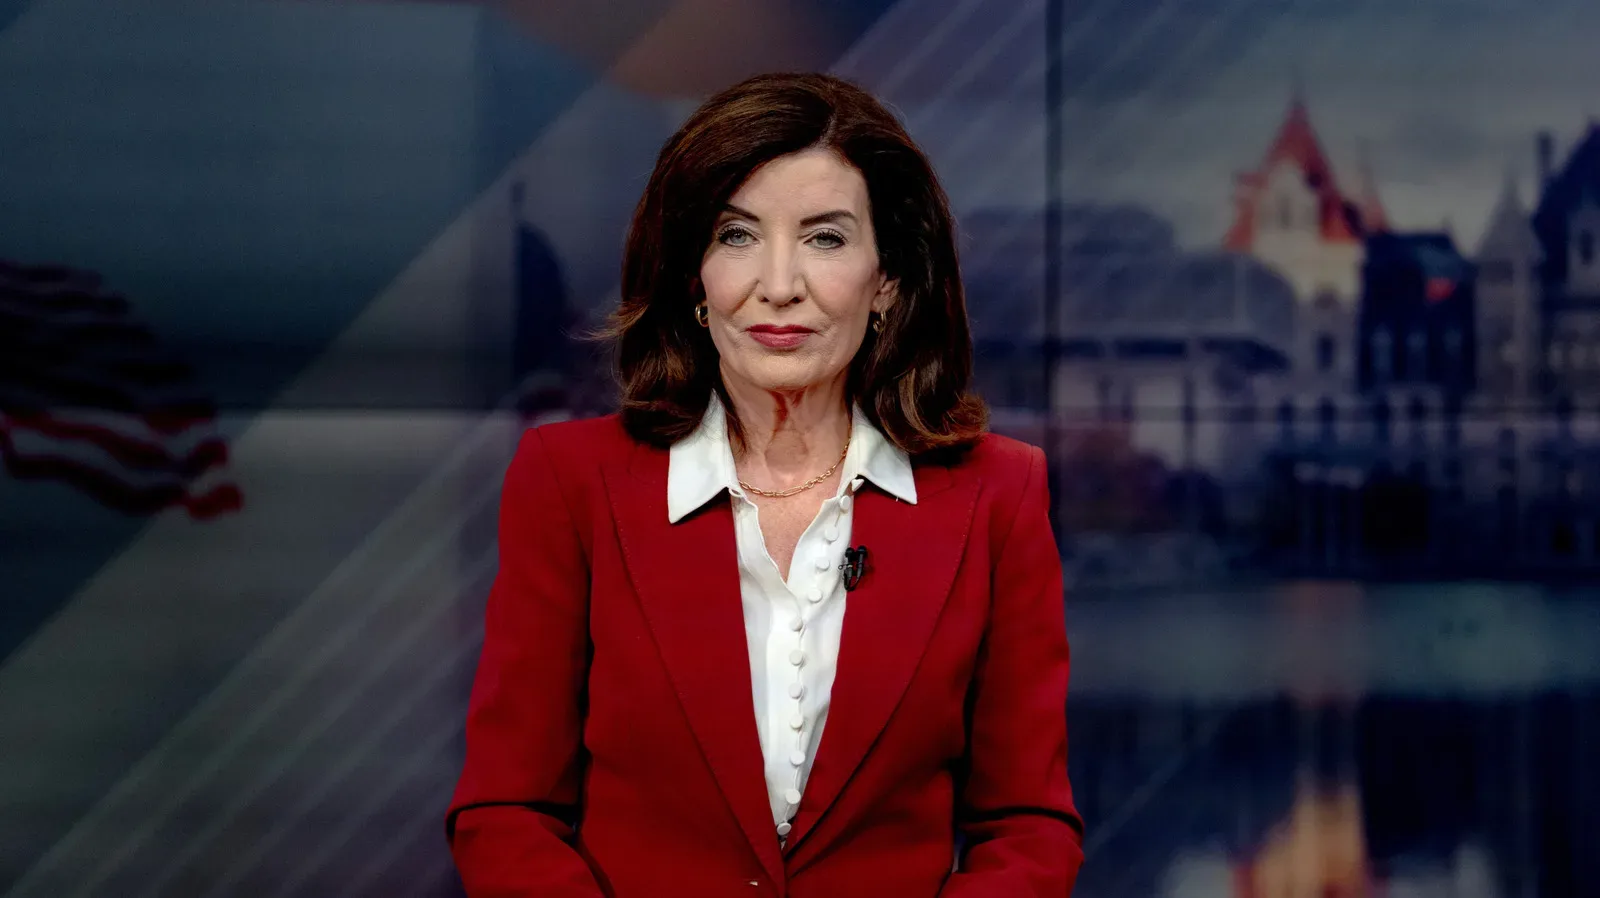
New York has launched a state-run effort to independently examine advanced artificial-intelligence systems rather than relying entirely on the companies that build them to describe their own safety work.
Governor Kathy Hochul’s new program places that work with the New York Center for AI Responsibility and Research at Binghamton University. More than 80 New York scientists are expected to contribute, with computing capacity supplied through Empire AI, the state’s $500 million public-private AI partnership.
The central idea is straightforward, even if the practical work will be difficult: developers can publish assessments of their AI systems, but researchers outside those companies should be able to test claims, examine risks and produce evidence public officials can use when making decisions. Hochul framed the rationale bluntly: “The stakes are too high to simply take AI companies at their word.”
The initiative is described as the first state-run AI testing program in the United States. Its remit includes testing advanced systems, studying their risks and investigating responsible uses in fields including medicine and scientific discovery.
What independent AI testing means
Independent testing means evaluation conducted by researchers who are not simply accepting a developer’s internal conclusions as final. In this case, the state is establishing a research-centered process through Binghamton University rather than leaving assessment solely in the hands of AI companies.
That distinction matters because AI safety is not a single checkbox. An advanced AI system may be assessed for many kinds of behavior and potential harm, and the evidence behind a company’s claims can affect policy choices. The stated purpose of New York’s center is not only to identify risks, but also to provide evidence that public officials can use.
The announcement does not specify a fixed menu of tests, individual models, or a public grading system. It would therefore be premature to assume the center will issue consumer-style scores, certify particular systems, or routinely inspect every AI product available in the state. What is clear is the intended division of responsibility: the center will conduct research and testing, while government officials may use its findings to inform decisions.
That could make the program more meaningful than a disclosure regime alone. A transparency report can tell the public what a company says it did. An independent research program is intended to give officials another basis for assessing those claims and the risks surrounding an advanced system.
Why computing power is part of the story
Testing sophisticated AI can require substantial computing resources. New York says the center will use computing power from Empire AI, its $500 million public-private AI partnership. That resource is important because an independent research group needs practical capacity to perform technical work on the systems it is permitted to study.
In plain terms, computing power refers to the processing resources needed to run demanding computational tasks. AI development and evaluation can be resource-intensive, particularly for advanced systems. Providing researchers with access to shared state-backed infrastructure is one way to reduce the gap between a public-interest research effort and well-resourced private developers.
The announcement does not detail how Empire AI’s capacity will be allocated, what specific testing methods the center will use, or whether every participating scientist will work directly with the same systems. Those are operational questions that may determine how broad and repeatable the eventual evaluations can be. For now, the confirmed point is that Empire AI will supply the computing support for the center’s work.
The RAISE Act creates a disclosure baseline
New York’s testing effort sits alongside the state’s RAISE Act, which Hochul signed last year. The law requires large AI developers to register with the state by January 1, 2027. From that point, covered companies must publish safety frameworks and transparency reports, and they must report critical safety incidents within 72 hours.
A safety framework is, broadly, a company’s structured approach to identifying and managing safety concerns. A transparency report is a disclosure intended to provide outside parties with information about the company’s practices or system-related issues. The announcement does not spell out the precise contents that will appear in every report, but the new requirements are designed to make more information available than would otherwise be public.
The 72-hour incident-reporting requirement is especially notable. It creates a defined window for reporting a critical safety incident after it occurs. The available information does not define every event that qualifies as critical, so the significance of that rule will depend on how the law’s requirements are applied. Still, its purpose is clear: potentially serious safety events should not remain undisclosed indefinitely.
Registration, safety frameworks, transparency reports and incident notifications do not automatically establish that an AI system is safe. They instead create channels through which the state can learn more about developers and their systems. The new Binghamton-based center is positioned as a complementary effort: disclosure may make information available, while independent researchers can analyze and test what is available.
The program’s key limitation: unreleased systems
New York’s model also has an important boundary. The center can only study information and systems that AI companies disclose publicly. That means it cannot fully close the gap around unreleased models or material companies have not made available.
This is a major practical distinction. An evaluator can only assess the system, documentation and access it has. If a model is not public, or if relevant details are not disclosed, an outside state-run research center has less ability to examine it. The RAISE Act is meant to improve the disclosure picture for large developers, but it does not give the program complete visibility into unreleased work.
That limitation should shape expectations. The program is not being presented as a mechanism that can inspect every AI system in development before anyone else sees it. Instead, it creates an independent state-supported research capacity for advanced systems that can be examined, while the RAISE Act pushes larger developers toward greater reporting and transparency beginning in 2027.
There is still value in that narrower scope. Publicly available systems and disclosures can be consequential in their own right, and a state with its own research infrastructure may be better placed to evaluate available evidence than one that has no dedicated testing operation at all. But public access is not the same thing as comprehensive access, and the distinction should remain front and center when judging what the initiative can accomplish.
Responsible-use research is broader than risk testing
The center’s assignment is not limited to identifying dangers. New York also says it will examine how AI can be used responsibly in medicine and scientific discovery. That dual role matters because AI policy is not only about restricting harmful conduct; it is also about understanding where systems may be useful and what responsible deployment should require.
Responsible use does not mean that a technology is automatically appropriate in every context. It means studying applications with attention to the risks and safeguards relevant to their use. The announcement identifies medicine and scientific discovery as areas of interest, but does not name particular tools, projects, institutions or outcomes. Those details should not be assumed.
For technology audiences, including people who follow AI’s growing presence around consumer software and entertainment, the broader lesson is that evaluation capacity matters. The debate is not merely whether a company includes AI in a product. It is also whether there is enough information for public institutions and independent researchers to assess claims, understand risks and make informed choices. That question will continue to matter as technology companies shape the platforms people use every day, from software ecosystems to gaming services. For one example of how platform decisions can directly affect users, see the changes to PlayStation Plus PC access.
What to watch next
The immediate development is the creation of the New York Center for AI Responsibility and Research and its role in the state’s independent-testing plan. The next major policy date in the information provided is January 1, 2027, when large AI developers are required to register under the RAISE Act and begin meeting its publication and incident-reporting obligations.
Several practical questions remain open. The announcement does not say which advanced systems will be examined first, how results will be presented, how researchers will obtain access to systems, or what specific findings would lead officials to take particular action. It also does not eliminate the disclosure limitation for unreleased models.
Even so, New York is building a notable state-level structure: researchers at Binghamton University, participation from more than 80 scientists, computing support from Empire AI, and a forthcoming legal disclosure framework for large developers. The approach does not promise total visibility into the AI industry. It does establish a public-interest effort to test the work that can be examined, analyze its risks and give officials evidence beyond companies’ own accounts.